The Cyrillic Font Our CSS Stack Never Reached
Our declared font stack hid an unexpected glyph supplier, so we checked rendered families and kept the historical build fix separate from browser coverage

Expert insights from Pharos Production on software engineering, FinTech and emerging technologies
Pharos Production's engineering team publishes technical guides and business analysis on FinTech, blockchain, Web3 and full-stack development. With 90+ engineers, 110+ apps delivered since 2013 and a 5/5 Clutch rating (2026), our senior developers and architects from Las Vegas and Kyiv offices share production-tested approaches and real project experience.
Technical deep-dives written by our senior engineers. Covers Web3 architecture, smart contract development, blockchain infrastructure, API design patterns and DevOps practices. Each article includes production-tested code examples and architecture decisions from real Pharos Production projects.
Market analysis and strategic perspectives for CTOs, product owners and startup founders. Covers FinTech market trends, regulatory landscape changes, technology adoption patterns and ROI frameworks for custom software investments. Data-backed analysis with industry benchmarks and forecasts.
Early-stage research on AI/ML integration, decentralized identity, zero-knowledge proofs, cross-chain interoperability and next-generation cloud architectures. Written by engineers actively building with these technologies across our 110+ delivered applications.
Criteria-based evaluation frameworks for founders choosing a development partner. Each guide covers what to look for, red flags to avoid and how Pharos meets the criteria.
Our declared font stack hid an unexpected glyph supplier, so we checked rendered families and kept the historical build fix separate from browser coverage
A dark gallery column inherited light borders until aliases and portal containers respected its scope, with separate token and rendered checks
Qualification decides how far you can rely on a software partner's evidence. It never moves responsibility off the regulated company. The guide applies GxP vendor qualification to a custom software development partner under EU GMP, ICH Q10 and PIC/S guidance, uses FDA and EMA texts where they fit and gives the steps, 25 questions by function, red flags and a weighted scoring template.
GxP software development seen from the builder's side: how a development team produces validation evidence inside its delivery pipeline, from requirement traceability and risk-based testing to change control and release records. The guide maps data integrity controls to 21 CFR Part 11 and EU GMP Annex 11 and includes a RACI that leaves validation with the client's QA.
Pharmaceutical companies run a different class of software at each stage of the value chain, from lab notebooks and EDC to safety databases and batch records. Our reading of this map is that most stages run on commercial systems each company validates for its own use, with custom work around them.
E2B R3 is the ICH format for moving individual case safety reports between safety databases as HL7 version 3 XML. The guide explains what changed from R2 and how a message is built, then compares FDA and EMA requirements and closes with an implementation checklist for engineering teams.
A technical account of Ludo's Web3 reputation platform, covering transaction ingestion, project analysis, search, cross-chain identity and the delivery infrastructure behind its dual-engine architecture.
Our audio pipeline used 10-minute model requests and 60-to-120-second retrieval fragments, with stored segments allowing reindexing without another speech call
The intended slide ranked first but fell below our retrieval cutoff. Earlier FDA calibration and a language probe explain why the threshold did not transfer.

A hosted model accepted our request format but leaked reasoning markers into citation parsing. The case traces capabilities, stream errors and separate speech.
About 15 minutes after a successful two-tab refresh, one credential triggered reuse handling. Our grace-window fix made both tabs converge on the same pair.
Our chat-history implementation used an atomic answer claim, conditional terminal writes and conversation locks to handle Stop, Retry and concurrent edits.
A 5% frame-change threshold missed seven synthetic slide transitions; revised region rules found the boundaries while exposing seven clipped webinar inserts.
Figures and recordings changed citation fields, history parsers and page-based progress, with code checks recorded separately from browser verification
Weights of 0.10 to 5.00 reordered surviving results but could not rescue a source outside raw top-k or below the similarity cutoff in our first retrieval policy
Our source lifecycle separated active retrieval from saved citation snapshots, preserving history after replacement while deleted files could return 404
All 33 checked table rows had exact cells, but a live answer used the wrong device column despite good page-level OCR and retrieval scores
Our first index used 1024-dimensional dense vectors, with a serving constraint, a versioned collection alias and a deliberately limited retrieval milestone
Our synthetic interview scored about 1.4% WER, while a separate FDA recording contained four FAIRS substitutions that the attention rules did not flag
Two readings flagged a unit error in our six-figure spike, while the later 22-figure run showed why numeric disagreement remained a limited inspection aid

A 31.3-second recording reported a 43.1-second bookmark, so our test generator needed checking before it could judge model timing and retrieval behavior
A patient-specific answer passed our citation parser while exceeding its sources, exposing the gap between source markers and claim support in a September test
Choose between fixed implementation, governed upgrades and migration from product requirements. Use a scenario matrix and permission register to record who can change the system and what remains unavailable.
Build operate transfer hands a vendor-built engineering team to the client, but for a team that is itself situated in Kyiv the EU and UK rules that move staff automatically do not apply. This guide explains how consent, a share purchase or Article 36-1 of the Labor Code decides who employs each engineer and how to keep the IP chain intact.
An ML model rollback restores the last validated release, but the previous model behaves as it did only if its features, preprocessing, threshold and serving runtime come back with it. The guide below covers the pin manifest, the choice between rollback, roll through, retraining and fallback, drift triggers calibrated by batch size and how to rehearse the path.
Authorize a mainnet release through a versioned manifest and ordered checks. The runbook assigns owners, required evidence and stop conditions before deployment and before enabling user activity.
CMS-0057-F requires payers to run a Prior Authorization API on FHIR R4, US Core and SMART and only recommends the Da Vinci CRD, DTR and PAS guides, while since October 1, 2026 certification to 45 CFR 170.315(g)(31)-(33) has required CRD 2.2.1, DTR 2.2.0 and PAS 2.2.1. This guide maps each component to its builder, governing text and failure mode, with a version matrix, conformance testing and build orders for both sides.
Payment orchestration retry logic decides whether a declined payment is tried again, when, on which route and with what changes. This guide maps Visa's four decline categories to retry and routing decisions, explains why cascading is not settled by the rules, treats SCA soft declines as a step-up and keeps every attempt idempotent.
Popularity bias makes a recommender show already popular items more often than users' tastes justify, and retraining on the resulting clicks makes it worse. This guide computes popularity lift, exposure Gini, coverage, novelty and miscalibration from serving logs, ranks the fixes by engineering cost and covers what the DSA asks of recommender systems.
Link each smart contract requirement to an expected result, evidence and reviewer. The escrow matrix covers permissions, terminal states, expiry, pause behavior, transfer failure and unpaid obligations.
IBM i insurance integration connects mobile quote, policyholder portal, broker API, payment and analytics channels to a policy administration system on IBM i without a rewrite. This guide maps each channel to a native mechanism, keeps endorsements and payments inside the existing RPG or COBOL programs and names the risk each path carries under the documented constraints of IBM i and its integration tools.
LDAR software for an EU oil or gas operator is the system of record behind the leak detection and repair program that Regulation (EU) 2024/1787 requires. This guide sets out the component, survey, leak, repair, delay and flare records the Regulation implies, the 5-day and 30-day repair clocks and how versioned rule tables absorb implementing acts still to come.
Evaluate a smart contract provider through delivery evidence, actual project contribution and operational authority. Use the filled escrow RFP to align proposals before comparing their prices.
EASA sets no single retention period for aircraft maintenance records. This guide maps each record class under Part-M, Part-145 and Part-CAMO to its rule, its holder and its clock, then turns the rules into build requirements for a records system: append-only corrections, CRS records bound to an identifiable signatory, per-record retention and exports that carry every clock through a change of operator or CAMO.
A vendor-neutral engineering comparison of the four ways a fleet or app platform gets vehicle data: dongle PIDs under SAE J1979, J1979-2 OBDonUDS vehicles, OEM connected-car APIs and raw CAN logging with DBC decoding, with a criteria matrix for choosing between them, the backend ingestion shape and data-quality traps of each, dongle security controls and the EU Data Act rule on who may ask for vehicle data.
A driver location tracking system carries a phone's location fix to two readers, the rider's map and the dispatch index. This guide follows the fix through background limits on Android and iOS, sampling by driver state, the transport and reconnect model, capacity sizing, an H3 cell index, map matching and nearest-driver lookup, and closes with what the EU Platform Work Directive means for collection and human review.
A build guide for the layer between a logistics platform and its carriers: one canonical shipment event model, a status mapping table that places generic parcel API statuses, LTL EDI 214 status messages and DCSA Track and Trace events side by side, per-carrier adapters, push delivery with a reconciliation poll, idempotent handling of duplicate and out-of-order events and detection of shipments that stop reporting.
A payment reconciliation engine proves that every movement in a platform's ledger also happened at the bank and, where a PSP carried it, at the PSP. The design below normalizes all three legs into one event model, matches on references before tolerances, posts fees and chargebacks separately and turns every unexplained difference into a typed break with an owner.
Build a smart contract estimate around accepted deliverables. A hypothetical escrow budget shows engineering effort, an upgrade option and the external costs that still need quotes before launch.
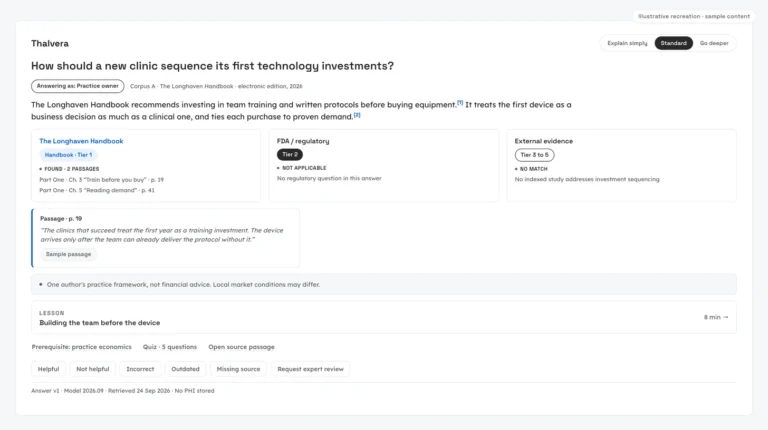
Before any model wrote an answer, our own mockups had invented citations. We redesigned an aesthetic-medicine learning platform so that every claim cites a printed page and every gap in its knowledge becomes a designed screen.
EIP-6963 does not replace window.ethereum, it adds a race-free discovery channel next to it. This guide works through what a dApp actually has to do at each layer of a wallet connection: EIP-1193's provider interface and its five events, a WalletConnect Sign v2.0 session whose granted namespace can differ from what was requested, a SIWE sign-in bound to an address and a domain, ERC-1271 and ERC-6492 signature verification for smart and counterfactual accounts, capability detection before a batched call and what EIP-7702 delegation means for a signature check written to assume every connected address is a plain externally owned account.
This guide treats a rate manual as a layered composite rather than a single document, drawing on the NAIC's own Product Filing Review Handbook, and works through the seven components a rating engine needs to make that composite queryable at run time, from effective-dated rate tables and factors keyed on the current term's effective date through the parity and regression testing that catches drift from the filed manual before a regulator or an audit does.
IPFS's own documentation is direct that a gateway URL is not the canonical address for NFT data, and EIP-4906 defines the events that tell a marketplace when metadata actually changed rather than merely moved. This guide works through where token metadata and media actually live, tokenURI under EIP-721 and uri with {id} substitution under EIP-1155, a five-option storage decision matrix (fully on-chain, IPFS with redundant pinning, Arweave, an HTTPS server, hybrid) and the failure modes a rushed build can run into: pin loss, gateway shutdown, mutable HTTPS metadata and a reveal whose rarity map can leak before it goes public.
ONE Record replaces sending a shipment record with publishing it once and granting access by URI, revocable at any time. This guide works through the model behind that standard: the logistics ontology and where its class hierarchy actually breaks, JSON-LD as the serialization, the API surface from creation to audit trail, subscriptions and access delegation, the published Cargo-XML migration path and the version and vocabulary conflicts a real integration hits inside the specification itself.
Article 77 of the EU Batteries Regulation requires an electronic record for LMT, industrial and electric-vehicle batteries, and the record is harder to design than it looks. This guide works through the decisions a platform makes when it implements it: why one passport belongs to one battery instance rather than one model, how three access tiers become an authorization model, where custody of the record moves across a battery's life and where a durability figure actually comes from.
Google Cloud's own migration guidance states the constraint every cut-over plan has to accept: genuinely zero downtime is impossible. This guide works through the decision a legacy data migration actually turns on, big bang against outbox-based trickle against log-based change data capture, why a dual write without a transactional outbox can silently diverge two databases, reconciliation tiered from row counts to field-level checks and the rehearsal and rollback discipline AWS's own cutover guidance describes.
What a first-party platform has to get right when it reads an IAB TCF TC String: three version counters that are not the same number, purpose bitfields indexed from zero while purposes are numbered from one, a vendor list that must be pinned to the version the string names rather than to the newest one, an event-driven read path on web and in app and a consent log that keeps the string itself.
A HACCP plan is not a document a platform stores. Treated as a data model it becomes a set of entities: hazards joined to process steps with their reasoning, critical limits that carry a version history, monitoring records naming a person and a device, corrective action as a workflow with states, verification events that point at the records they reviewed and retention expressed as a rule with a named party rather than a number.
What a fitness platform has to build to accept device uploads and hand them back: a decoder that reads definition messages before data, a timestamp path that knows the FIT epoch from a relative value, an integrity check the specification owner makes the case for skipping on activity files, an identity key that survives a re-upload and an export path that is honest about what TCX and GPX drop.
What an MVNO or a connectivity platform has to build to move a profile from an SM-DP+ into a subscriber's eUICC: the consumer architecture and the components that own each step, an activation code whose positional fields fail quietly, two client paths that decompose that code differently and the authorization each platform demands before your app may download anything. With the failure we expect named at every step.
Inside the blog
Every article on this blog comes from production experience - not theory. Our engineers write about problems they solved on real projects across FinTech, healthcare, Web3 and enterprise platforms. You get architecture decisions, code patterns and integration strategies tested under actual business constraints.
All content is reviewed by CTO Dmytro Nasyrov before publication. We prioritize depth over frequency: each piece covers a specific technical challenge with enough context for you to apply the solution in your own stack. Whether you are evaluating a technology or debugging an architecture, these articles save you research time.
Common questions about the Pharos Production engineering blog.
Type to filter questions and answers. Use Topic to narrow the list.
Showing all 4
No matches
Try a different keyword, change the topic or clear filters
The Pharos Production engineering blog covers FinTech trends, Web3 and blockchain development, custom software architecture and emerging technology insights. Articles are written by our team of 90+ engineers from Las Vegas and Kyiv offices with hands-on production experience.
All articles are written by senior engineers and architects at Pharos Production and reviewed by CTO Dmytro Nasyrov. The team brings 13+ years of production experience across 28+ industries including FinTech, healthcare and Web3.
Pharos Production publishes new articles regularly based on industry developments, project learnings and technology releases. Each article goes through technical review and fact-checking before publication.
Subscribe or check back for the latest insights on software development.
Yes. All articles on the Pharos Production blog are freely accessible and may be cited with attribution. For deeper technical consultation or custom research on a topic covered in our articles, contact our engineering team directly.
Achieve them with minimized risk through our bespoke innovation capabilities
Contact us today to discuss your project. We're ready to review your request promptly and guide you on the best next steps for collaboration
Same dayWe're committed to keeping your information confidential, so we'll sign a Non-Disclosure Agreement
1 dayAfter we chat about your goals and needs, we'll craft a comprehensive proposal detailing the project scope, team, timeline and budget
3-5 daysLet's connect on Google Meet to go through the proposal and confirm all the details together!
1-2 daysAs soon as the contract is signed, our dedicated team will jump into action on your project!
Same dayThanks for the request!
We typically reply within 24 hours