Skip to content
218 articles & insights

Software Development Blog

Expert insights from Pharos Production on software engineering, FinTech and emerging technologies

Pharos Production's engineering team publishes technical guides and business analysis on FinTech, blockchain, Web3 and full-stack development. With 90+ engineers, 110+ apps delivered since 2013 and a 5/5 Clutch rating (2026), our senior developers and architects from Las Vegas and Kyiv offices share production-tested approaches and real project experience.

What you'll find here

Engineering Insights

Technical deep-dives written by our senior engineers. Covers Web3 architecture, smart contract development, blockchain infrastructure, API design patterns and DevOps practices. Each article includes production-tested code examples and architecture decisions from real Pharos Production projects.

Business Insights

Market analysis and strategic perspectives for CTOs, product owners and startup founders. Covers FinTech market trends, regulatory landscape changes, technology adoption patterns and ROI frameworks for custom software investments. Data-backed analysis with industry benchmarks and forecasts.

Emerging Technologies

Early-stage research on AI/ML integration, decentralized identity, zero-knowledge proofs, cross-chain interoperability and next-generation cloud architectures. Written by engineers actively building with these technologies across our 110+ delivered applications.

Vendor Evaluation Guides

Criteria-based evaluation frameworks for founders choosing a development partner. Each guide covers what to look for, red flags to avoid and how Pharos meets the criteria.

Latest Software Development Articles

A still life on a white desk of ten printed company profile sheets laid in a row, a smaller pile of six sheets set aside under a blue binder clip, a hardware wallet signing device and a bare single-board validator node with an ethernet cable beside them.

Blockchain Development Companies: The Top 10 for 2026

17 min read

This page profiles ten blockchain development companies with founding year, headcount, headquarters and specialization. Every fact is attributed to the source it came from: that company's own site, its LinkedIn company page or its GoodFirms profile. Where those sources disagree, the disagreement is stated in that company's entry rather than resolved by guessing, and six…
Hands and shoulders of an IT evaluator at a conference table ticking a row on a printed feature-by-feature scorecard that lies between two identical open laptops, each showing a soft out-of-focus admin console layout, a blue lanyard resting on the table.

Claude Enterprise vs OpenAI Enterprise

5 min read

Choosing between Claude Enterprise and OpenAI Enterprise is one of the most consequential AI platform decisions an engineering organization makes in 2026. Both platforms offer team-wide deployment with admin controls, SSO and compliance features. The differences are in context handling, tool integration architecture, safety approach and pricing model. This comparison evaluates both platforms across the…

Tight close-up of a payments test bench: a printed company profile sheet with one line flagged by a blue paper tab, a card payment terminal and three blank white test bank cards fanned beside it on a white desk.

FinTech Development Companies: The Top 10 for 2026

23 min read

This page profiles ten FinTech development companies with founding year, headcount, headquarters and specialization. Every fact is attributed to the source it came from: that company's own site or its public LinkedIn company page. Where those sources disagree, the disagreement is stated in that company's entry rather than resolved by guessing, and candidate companies excluded…

Pharma Software Development Companies

Pharma Software Development Companies

33 min read

Of the eleven pharma software development companies profiled here besides the publisher, three describe delivered GxP work on the pages read for this list: TTMS, ScienceSoft and BGO LifeScience. Each of the 12 entries gives founding year, headcount, headquarters and specialization and reports what the company's own pages show on seven weighted criteria, from evidence…

An aircraft technician in a hangar signing a paper work card on a clipboard beside an engine cowling.

Aircraft Maintenance Records

Dmytro Nasyrov, Founder & CTO 22 min read

EASA sets no single retention period for aircraft maintenance records. This guide maps each record class under Part-M, Part-145 and Part-CAMO to its rule, its holder and its clock, then turns the rules into build requirements for a records system: append-only corrections, CRS records bound to an identifiable signatory, per-record retention and exports that carry every clock through a change of operator or CAMO.

An OBD-II dongle plugged into a car's under-dash diagnostic port, with a phone mount nearby.

OBD-II Data Access

Dmytro Nasyrov, Founder & CTO 21 min read

A vendor-neutral engineering comparison of the four ways a fleet or app platform gets vehicle data: dongle PIDs under SAE J1979, J1979-2 OBDonUDS vehicles, OEM connected-car APIs and raw CAN logging with DBC decoding, with a criteria matrix for choosing between them, the backend ingestion shape and data-quality traps of each, dongle security controls and the EU Data Act rule on who may ask for vehicle data.

A courier on a scooter checking a phone in a handlebar mount at a curb before starting a shift.

Driver Location Tracking

Dmytro Nasyrov, Founder & CTO 21 min read

A driver location tracking system carries a phone's location fix to two readers, the rider's map and the dispatch index. This guide follows the fix through background limits on Android and iOS, sampling by driver state, the transport and reconnect model, capacity sizing, an H3 cell index, map matching and nearest-driver lookup, and closes with what the EU Platform Work Directive means for collection and human review.

A shipping container seal and a handheld barcode scanner resting on a dock office desk.

Carrier Integration Layer

Dmytro Nasyrov, Founder & CTO 22 min read

A build guide for the layer between a logistics platform and its carriers: one canonical shipment event model, a status mapping table that places generic parcel API statuses, LTL EDI 214 status messages and DCSA Track and Trace events side by side, per-carrier adapters, push delivery with a reconciliation poll, idempotent handling of duplicate and out-of-order events and detection of shipments that stop reporting.

A finance operations analyst comparing a printed bank statement with a laptop's ledger layout in a bright office.

Payment Reconciliation Engine

Dmytro Nasyrov, Founder & CTO 22 min read

A payment reconciliation engine proves that every movement in a platform's ledger also happened at the bank and, where a PSP carried it, at the PSP. The design below normalizes all three legs into one event model, matches on references before tolerances, posts fees and chargebacks separately and turns every unexplained difference into a typed break with an owner.

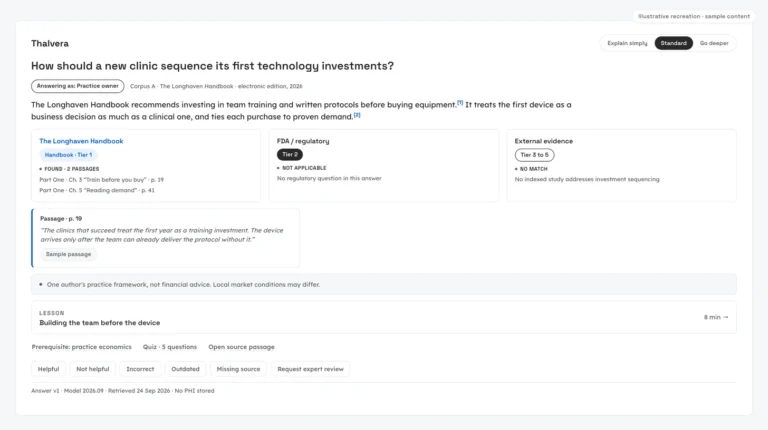
An illustrative AI answer screen with a cited summary, three source classes and feedback controls

AI Citation UX for Aesthetic Medicine: Our Mockups Hallucinated Before the Model Did

Dmytro Nasyrov, Founder & CTO 28 min read

Before any model wrote an answer, our own mockups had invented citations. We redesigned an aesthetic-medicine learning platform so that every claim cites a printed page and every gap in its knowledge becomes a designed screen.

An engineer scanning a laptop's wallet-pairing QR code with a phone during a WalletConnect Sign integration test.

dApp Wallet Connection

Dmytro Nasyrov, Founder & CTO 19 min read

EIP-6963 does not replace window.ethereum, it adds a race-free discovery channel next to it. This guide works through what a dApp actually has to do at each layer of a wallet connection: EIP-1193's provider interface and its five events, a WalletConnect Sign v2.0 session whose granted namespace can differ from what was requested, a SIWE sign-in bound to an address and a domain, ERC-1271 and ERC-6492 signature verification for smart and counterfactual accounts, capability detection before a batched call and what EIP-7702 delegation means for a signature check written to assume every connected address is a plain externally owned account.

A filed rate manual binder open beside a printed rate table stamped with its effective date, on an actuarial analyst's desk.

Insurance Rating Engine

Dmytro Nasyrov, Founder & CTO 20 min read

This guide treats a rate manual as a layered composite rather than a single document, drawing on the NAIC's own Product Filing Review Handbook, and works through the seven components a rating engine needs to make that composite queryable at run time, from effective-dated rate tables and factors keyed on the current term's effective date through the parity and regression testing that catches drift from the filed manual before a regulator or an audit does.

A small pinning-node server on a rack shelf beside a printed content-hash reference sheet, with ethernet cables running to it.

NFT Metadata Storage

Dmytro Nasyrov, Founder & CTO 20 min read

IPFS's own documentation is direct that a gateway URL is not the canonical address for NFT data, and EIP-4906 defines the events that tell a marketplace when metadata actually changed rather than merely moved. This guide works through where token metadata and media actually live, tokenURI under EIP-721 and uri with {id} substitution under EIP-1155, a five-option storage decision matrix (fully on-chain, IPFS with redundant pinning, Arweave, an HTTPS server, hybrid) and the failure modes a rushed build can run into: pin loss, gateway shutdown, mutable HTTPS metadata and a reveal whose rarity map can leak before it goes public.

A ground handler scanning a shipment label and granting a colleague on-screen access to the record instead of handing over a paper waybill.

IATA One Record Integration

Dmytro Nasyrov, Founder & CTO 19 min read

ONE Record replaces sending a shipment record with publishing it once and granting access by URI, revocable at any time. This guide works through the model behind that standard: the logistics ontology and where its class hierarchy actually breaks, JSON-LD as the serialization, the API surface from creation to audit trail, subscriptions and access delegation, the published Cargo-XML migration path and the version and vocabulary conflicts a real integration hits inside the specification itself.

A quality engineer checking an individual battery pack's freshly printed serial label against a per-unit tracking list, with the model specification binder open beside it.

Battery Passport Data Model

Dmytro Nasyrov, Founder & CTO 19 min read

Article 77 of the EU Batteries Regulation requires an electronic record for LMT, industrial and electric-vehicle batteries, and the record is harder to design than it looks. This guide works through the decisions a platform makes when it implements it: why one passport belongs to one battery instance rather than one model, how three access tiers become an authorization model, where custody of the record moves across a battery's life and where a durability figure actually comes from.

A migration team in a cutover war room watching a replication-lag dashboard, one engineer holding a phone ready to call a rollback.

Legacy Data Migration Strategy

Dmytro Nasyrov, Founder & CTO 24 min read

Google Cloud's own migration guidance states the constraint every cut-over plan has to accept: genuinely zero downtime is impossible. This guide works through the decision a legacy data migration actually turns on, big bang against outbox-based trickle against log-based change data capture, why a dual write without a transactional outbox can silently diverge two databases, reconciliation tiered from row counts to field-level checks and the rehearsal and rollback discipline AWS's own cutover guidance describes.

An engineer inspecting decoded consent string fields on a monitor at a desk.

TCF Consent String

Dmytro Nasyrov, Founder & CTO 20 min read

What a first-party platform has to get right when it reads an IAB TCF TC String: three version counters that are not the same number, purpose bitfields indexed from zero while purposes are numbered from one, a vendor list that must be pinned to the version the string names rather than to the newest one, an event-driven read path on web and in app and a consent log that keeps the string itself.

A food safety officer reviewing HACCP monitoring records on a tablet in a commercial kitchen.

HACCP Software Requirements

Dmytro Nasyrov, Founder & CTO 20 min read

A HACCP plan is not a document a platform stores. Treated as a data model it becomes a set of entities: hazards joined to process steps with their reasoning, critical limits that carry a version history, monitoring records naming a person and a device, corrective action as a workflow with states, verification events that point at the records they reviewed and retention expressed as a rule with a named party rather than a number.

A bike computer and a sports watch on a workbench beside a laptop showing an uploaded activity.

FIT File Ingestion

Dmytro Nasyrov, Founder & CTO 20 min read

What a fitness platform has to build to accept device uploads and hand them back: a decoder that reads definition messages before data, a timestamp path that knows the FIT epoch from a relative value, an integrity check the specification owner makes the case for skipping on activity files, an identity key that survives a re-upload and an export path that is honest about what TCX and GPX drop.

An MVNO operations desk provisioning an eSIM profile onto a customer handset.

eSIM Provisioning Integration

Dmytro Nasyrov, Founder & CTO 20 min read

What an MVNO or a connectivity platform has to build to move a profile from an SM-DP+ into a subscriber's eUICC: the consumer architecture and the components that own each step, an activation code whose positional fields fail quietly, two client paths that decompose that code differently and the authorization each platform demands before your app may download anything. With the failure we expect named at every step.

An IFC spatial tree diagram rendered as a real building section model on a desk.

IFC Data Integration

Dmytro Nasyrov, Founder & CTO 20 min read

An IFC file can validate against the schema and still disagree with the last one about which storey a wall belongs to. This guide works through the decisions a construction platform makes when it ingests IFC: which encoding to accept, what identity is keyed on, how the spatial tree is discovered, where properties and quantities really live, how uploads are validated and how models are placed against each other.

A farm office desk preparing task data for isoxml integration with a machine terminal.

ISOXML Integration

Dmytro Nasyrov, Founder & CTO 20 min read

The two halves of an ISOXML integration that no standard hands you: the mapping between a task data set and a platform's own model, and the validation that stops a bad export before it reaches a cab. Around them, the two transfer directions, where Part 10 and Part 11 sit, the dictionary lookup behind every logged value, what a task controller functionality actually warrants and the import failures the AEF names.

Engineers reviewing an LTI Advantage integration launch from an LMS course page.

LTI Advantage Integration

Dmytro Nasyrov, Founder & CTO 20 min read

The platform half of an LTI Advantage integration, which the tool-side tutorials never cover: the identifiers a learning platform mints, the login it issues, the token it signs, the key set it publishes and the gradebook and roster endpoints it exposes. With the service table, the migration claim that keeps existing records attached and why the Complete certification level is required for platforms.

Crew controllers reviewing duty and rest timelines on a crew rostering software screen.

Crew Rostering Software

Dmytro Nasyrov, Founder & CTO 20 min read

What a crew rostering engine has to compute under EASA Subpart FTL: the acclimatization state it derives before any table can be read, the maximum flight duty period looked up in reference time, the cumulative duty limits held as rolling windows beside a calendar-year flight time total and standby, reserve and rest on their own counters. Around them, the duties and rest data model, recomputation on disruption and the audit trail every verdict needs.

Operators monitoring pipeline leak detection software on SCADA control room screens.

Pipeline Leak Detection Software

Dmytro Nasyrov, Founder & CTO 19 min read

Computational pipeline monitoring read as a software specification: the definition 49 CFR 195.2 gives it, the design rule at 195.134 and the operating rule at 195.444 that bind an operator to API RP 1130, the seven method families of section 4.1.2 with the data each one demands in engineering practice, plus the sensitivity against false alarms trade that no numerical performance standard in the regulation settles for you.

An industrial gateway cabinet running opc ua integration on a plant floor.

OPC UA Integration

Dmytro Nasyrov, Founder & CTO 20 min read

The four decisions that decide whether an OPC UA integration holds: a published companion specification or a custom nodeset; a decoder that reads structures instead of storing opaque bytes; subscriptions and queues sized against a server that revises what you ask for; certificates and roles that are administered rather than coded. Around them the northbound leg, the historian mapping and the gateway question.

A smartphone lying untouched beside a SIM card tray and a small network appliance in a mobile operator's ops corner.

CAMARA Network API Integration

Dmytro Nasyrov, Founder & CTO 18 min read

CAMARA Location Verification answers TRUE, FALSE or PARTIAL rather than a plain boolean, and a SIM Swap null can mean the operator would not disclose a date rather than no swap occurred. This guide works through the four CAMARA network APIs a product team actually integrates, the identity and consent layer behind all of them and the error model that treats its own published codes as incomplete by design.

A small server rack with a printed interval schedule in a charging depot, the row of charging stations beyond.

OpenADR Integration

Dmytro Nasyrov, Founder & CTO 18 min read

The two parts of an OpenADR integration that sit outside the certified VTN to VEN interface: how each OpenADR 3 event interval becomes an OCPP 2.0.1 SetChargingProfile, with a capacity ceiling and a per-transaction schedule stacked on one station, and what the platform does when the VTN stops answering. Around them, the VTN and VEN roles, registration and OAuth, reporting, 2.0b coexistence and certification as a process.

Customs import documents, a goods lines printout, a producer's emissions data sheet and a verifier's report assembled on an importer's compliance desk.

CBAM Annual Declaration

Dmytro Nasyrov, Founder & CTO 18 min read

In a CBAM annual declaration the certificate count is the embedded emissions after the carbon-price reduction and the free-allocation adjustment, and every other element of the filing is stated here as a data model with its article, its data source and its validation check.

A platform team checking a test house report and change record register beside a laptop showing the game lobby.

UKGC Technical Standards

Dmytro Nasyrov, Founder & CTO 19 min read

A requirement-by-requirement reading of the Gambling Commission's Remote gambling and software technical standards as platform behavior: what RTS 1 to 17 ask the software to do, which rows an approved test house certifies and which the licensee tests itself, the ISO/IEC 27001:2022 security requirements and their audit, the GAMSTOP check cadence and how the Malta Gaming Authority's system audit compares.

A trust and safety analyst checking a product's warning label and responsible person card beside a colleague's listing screen.

GPSR Online Marketplaces

Dmytro Nasyrov, Founder & CTO 18 min read

A build guide to Regulation (EU) 2023/988 for marketplace platforms: the four listing information blocks and the conditional responsible-person rule as seller-onboarding validation, the two contact points, the clocks on authority orders and notices with their working-day outer bounds, Safety Gate ingest, the recall-notice pipeline with the seven elements Article 36(2) lists, some of them conditional and an evidence log derived from the duties to inform, each mapped to its article.

Operations staff at a coverholder checking a printed bordereau against the policy system before the monthly submission.

Bordereaux Reporting

Dmytro Nasyrov, Founder & CTO 19 min read

Lloyd's mandates the data set and the Delegated Data Manager is listed as an elective LIMOSS service. A procedural guide to bordereaux reporting for coverholders and MGAs: the risk, premium and claims bordereaux and who produces and receives them, the Coverholder Reporting Standards field set stated by version, then the pipeline from extraction through mapping, validation, exception handling and cadence to delivery and the audit trail.

An engineer checking a key rotation log against a printed authorization flow sheet beside a media server rack.

Secure HLS Delivery

Dmytro Nasyrov, Founder & CTO 20 min read

RFC 8216 spends exactly one sentence on protecting an HLS decryption key, and says nothing about who may ask for one. This guide works through the decisions that actually secure a stream: the key request as an authorization decision, signed manifests against signed segment URLs, CDN caching rules that can silently leak a key response and the boundary past which AES-128 stops helping and a licensed DRM system takes over.

A developer testing a build while wearing one XR headset, with several other headsets from different platforms resting on the bench beside them.

OpenXR Cross Platform Development

Dmytro Nasyrov, Founder & CTO 19 min read

Khronos's own specification defines OpenXR's extension model around one rule: every extension is optional per runtime, so a codebase has to query extensions with xrEnumerateInstanceExtensionProperties, and optional core features such as STAGE with their own enumeration call, before depending on them. This guide works through the decisions that follow from that rule: action-based input bound to interaction profiles instead of raw controller state, reference spaces with no shared origin, engine-level OpenXR coverage that depends on each engine's own gap list and why visionOS is a separate platform with no OpenXR runtime to target, not another runtime to detect.

Two printed listing sheets from different MLS systems for the same property, laid side by side with their differing local identifiers visible.

RESO Web API Integration

Dmytro Nasyrov, Founder & CTO 18 min read

RESO's own wiki defines ListingKey as a local key of the system that issued it, not the durable, cross-system identifier most integration plans assume. This guide works through the ten decisions a RESO Web API integration gets wrong on the second MLS: ModificationTimestamp polling against the EntityEvent alternative, a Lookup layer that resolves a local synonym back to one standard value and what a "RESO certified" server actually promises to expose.

A part filled paper identification form and a size self assessment sheet on a desk beside a laptop showing a plain sign in panel, a company registering with its national cybersecurity authority

NIS2 Entity Registration

Dmytro Nasyrov, Founder & CTO 19 min read

NIS2 puts two different filings behind one word. Member States build the list and require entities to submit identifying information for it, on a two-week update clock, while a narrower set of digital entity types files a longer record with its national authority, corrects it on a three-month clock and has it forwarded to ENISA without its IP ranges. This guide separates the two, marks who is bound by each, and shows what national portals add on top.

A management board reviewing a tabbed outsourcing contract at a boardroom table with a soft security operations dashboard on the wall screen behind, one member signing the accountability sheet

NIS2 Compliance Outsourcing

Dmytro Nasyrov, Founder & CTO 20 min read

NIS2 contains no prohibition on outsourcing any security measure, so the real question is which parts of Article 21 the market can supply and which acts sit with management bodies under Article 20 and the implementing regulation rather than with a provider. A decision guide for an entity whose scope is already settled, covering the supply chain duty that buying anything creates and the evidence a supervisory authority asks the entity, not the vendor, to produce.

A hotel revenue manager checking a wall mounted availability grid against a rack of room key cards in the back office, the inventory a channel manager keeps synced across channels

Hotel Channel Manager Integration

Dmytro Nasyrov, Founder & CTO 13 min read

Hotel channel manager integration as a catalog of failure modes: ARI drift, overbooking from inventory races, rate and room mapping errors, reservation desync and the certification gates standing between a connector and a live OTA channel.

A privacy operations employee at a desk cross-referencing a printed data-erasure request against several system record printouts, a wall calendar with one date circled behind them, resolving a GDPR erasure request that arrived through an EUDI Wallet

EUDI Wallet Data Deletion

Dmytro Nasyrov, Founder & CTO 15 min read

A wallet user taps erase and what reaches you is a GDPR Article 17 request. This is the boundary between the wallet's machinery and the controller's own obligations, the one-month clock the recital's word immediate does not shorten, and the refusal path most build estimates miss.

A payments operations employee at a back-office desk holding a smartphone showing a blurred wallet confirmation screen beside a monitor displaying a blurred transaction record and a card terminal printing a receipt, a payment service processing a wallet-presented SCA Attestation

EUDI Wallet SCA

Dmytro Nasyrov, Founder & CTO 13 min read

A wallet-presented SCA Attestation is an OpenID4VP presentation carrying transactional data, and TS12 states that its verified jti claim serves as the Authentication Code PSD2 requires for electronic payments. This guide walks a payment service through the processing order: reading type metadata, signing and encrypting the request, surviving the locale check, verifying the Key Binding JWT and gating on the amr array. Written throughout as a second acceptance path alongside an existing implementation, never as a replacement for one.

A phone showing a chat style layout resting beside a boarding pass and passport on a quiet desk, an AI travel agent assembling a flight booking

AI Travel Agent Development

Dmytro Nasyrov, Founder & CTO 13 min read

AI travel agent development for an OTA, TMC or booking platform: what a tool-calling agent can and cannot book today, how it stays grounded on live inventory, the guardrails a mis-booking risk requires and an evaluation protocol before launch.

A printed crypto-asset white paper open at its ruled sections with a separate summary sheet on top, beside a monitor showing a soft nested outline of tagged sections

MiCA White Paper Requirements

Dmytro Nasyrov, Founder & CTO 20 min read

The crypto-asset white paper under MiCA Title II is a disclosure document nobody approves and whose content the offeror is solely responsible for. This guide sets out who must draw one up and who is exempt from precisely which obligations, what Annex I forces into the document, the Inline XBRL format rule and its application date, and the notification, publication, modification and withdrawal clocks that run around it.

A compliance team assembling a crypto authorization application dossier from labelled binders against a printed document checklist, an application form open on a tablet

CASP License Application

Dmytro Nasyrov, Founder & CTO 18 min read

An item-by-item walkthrough of the MiCA CASP authorization file: the nineteen points of Article 62(2), what Delegated Regulation (EU) 2025/305 adds on top of them, the annex form and contact point set by the implementing regulation, and the completeness and assessment periods stated as rules rather than as a countdown.

Two colleagues in a video call room reading a printed client onboarding record during a call with a remote participant, illustrating reverse solicitation evidence under MiCA Article 61

Reverse Solicitation Under MiCA: The Article 61 Boundary

Dmytro Nasyrov, Founder & CTO 20 min read

The MiCA transitional period was over everywhere by 1 July 2026, earlier in Member States that shortened it. A third-country crypto firm serving EU clients without a CASP authorization now has exactly one legal basis left, Article 61 reverse solicitation, and two years of ESMA guidance have narrowed it to a keyhole. We work through the statute, the 26 February 2025 guidelines, the broker-model opinion on routing and letter-box entities and ESMA's freshest compliance table dated 10 July 2026, which shows Poland and Romania still without a designated authority for these guidelines ten days after grandfathering ended. Then we cover what an engineering team actually builds to prove a client showed up on its own.

A DMC operations team marking a wall departure calendar while reviewing a paper supplier contract at a desk with a wall map behind, the operational surface a tour operator platform has to encode

Tour Operator Software Development

Dmytro Nasyrov, Founder & CTO 13 min read

Tour operator software development as a phased migration off a legacy reservation system: supplier contracting, allotments and release rules, quotes and vouchers, data cutover and what the Package Travel Directive, both the 2015 text and the 2026 amendment, requires the platform to encode.

A compliance officer laying a thin national registration certificate beside a thick authorization decision on a desk, comparing two crypto authorization regimes against a hand ruled decision table

CASP vs VASP

Dmytro Nasyrov, Founder & CTO 19 min read

VASP is a supervisory label that appears nowhere in EU legislation, used by national regulators for firms on the anti-money-laundering registers the Fifth Anti-Money Laundering Directive required. CASP is an authorization under MiCA Title V with a defined service list and an EU passport. This guide sets the entity-level regimes side by side, including the electronic money institution license and the Article 60 notification route that removes the need for a CASP application for seven categories of already-licensed institution.

Close up of a secure door in a custody operations room with an access reader, a hand filled access log on a clipboard and a sealed cabinet for crypto-asset safekeeping.

MiCA Custody Requirements

Dmytro Nasyrov, Founder & CTO 14 min read

MiCA custody requirements mapped provision by provision: Article 70's safekeeping baseline for every CASP, Article 75's nine-paragraph custody rulebook, the three-limb segregation test, the liability cap at market value at time of loss and the evidence a CASP should have ready for each obligation.

Two distribution engineers laying out printed message sample sheets in sequence across a long desk, the Offer to Order message flow behind an airline NDC integration

NDC API Integration

Dmytro Nasyrov, Founder & CTO 10 min read

NDC API integration for a flight-booking platform: the Offer and Order message set message by message, aggregator versus direct connect, servicing after the sale and what IATA's own capability program actually measures.

Printed export inventory on a desk, permission lists beside a schema diagram, a catalog table and a network trust diagram

Data Act cloud switching requirements

Dmytro Nasyrov, Founder & CTO 18 min read

Article 30 of the EU Data Act splits a switching duty by capability, not by service-model label, and Article 2(37) defines functional equivalence in law while no published standard operationalises it into a threshold. This article works through the exemption gate, the export inventory beyond raw data and the escrow-and-rebuild record that stands in for the missing standard, including the correction most coverage misses: 12 January 2027 zeroes switching charges, not multi-cloud egress.

Two records of the same fund holdings compared side by side, a printed ledger listing and a bound shareholder register

Tokenized fund register reconciliation

Dmytro Nasyrov, Founder & CTO 18 min read

A tokenized fund runs two books, the ledger the token moves on and the shareholder register a transfer agent maintains, and three published regimes now say which one wins when they disagree, in two opposite directions. None of them says how anyone learns the two diverged, at what cadence or where the investor stands between a bad entry and its reversal.

Two printed clinical entries for the same event lying side by side on a hospital records desk, one carrying a stamped clinician initial and the other a plain unsigned system tag

AI Agent EHR Write Access

Dmytro Nasyrov, Founder & CTO 16 min read

A FHIR server may legally ignore the provenance header meant to prove who wrote an entry, a granted write scope only confirms a ceiling on what an agent might do and not what a server will accept, and neither settles whether the agent doing the writing has built a medical device.

An on-duty engineer standing at a desk with a phone handset lifted off its cradle and starting the first entry on a blank printed incident record form, the moment one of the AI Act reporting clocks starts running

AI Act Serious Incident Reporting

Dmytro Nasyrov, Founder & CTO 20 min read

The AI Act defines a serious incident in four alternative limbs and attaches three different reporting deadlines to them, and since 27 July 2026 the recipient of the report depends on who supervises the provider.

Two bound hardcover incident logbooks lying open side by side on one desk with visibly different column rulings and a separate pen resting in each, the two independent classification passes a financial entity runs under the AI Act and DORA

AI Act and DORA Overlap

Dmytro Nasyrov, Founder & CTO 19 min read

How the EU AI Act and DORA land on the same financial entity without either text citing the other, why Article 74(6) puts the AI file on the financial supervisor's desk, and what Articles 26(5), 26(6), 72(4) and 73(9) actually change.

A bank compliance officer reading from an open supplier manual while a colleague fills a single row on a wide ruled sheet whose other rows stay empty, the deployer side fundamental rights impact assessment owed by banks and insurers under the AI Act

AI Act Fundamental Rights Impact Assessment

Dmytro Nasyrov, Founder & CTO 23 min read

Article 27 of the AI Act puts the fundamental rights impact assessment on the deployer, names creditworthiness and life and health insurance pricing explicitly, and since July 2026 lets it cross-reference an existing data protection impact assessment.

Pharos Production - Stuck on a hard engineering problem? Our engineers write from production experience. If you need hands-on help, not just an article, reach out and describe the problem. Talk to engineering.

Why read our blog

Every article on this blog comes from production experience - not theory. Our engineers write about problems they solved on real projects across FinTech, healthcare, Web3 and enterprise platforms. You get architecture decisions, code patterns and integration strategies tested under actual business constraints.

All content is reviewed by CTO Dmytro Nasyrov before publication. We prioritize depth over frequency: each piece covers a specific technical challenge with enough context for you to apply the solution in your own stack. Whether you are evaluating a technology or debugging an architecture, these articles save you research time.

  • 110+ Apps delivered to production
  • 28+ Industries covered
  • 13+ Years of engineering experience

Blog FAQ

Last updated: Reviewed by: Dmytro Nasyrov

Common questions about the Pharos Production engineering blog.

  • What topics does the Pharos Production blog cover?

    The Pharos Production engineering blog covers FinTech trends, Web3 and blockchain development, custom software architecture and emerging technology insights. Articles are written by our team of 90+ engineers from Las Vegas and Kyiv offices with hands-on production experience.

  • Who writes the articles on this blog?

    All articles are written by senior engineers and architects at Pharos Production and reviewed by CTO Dmytro Nasyrov. The team brings 13+ years of production experience across 28+ industries including FinTech, healthcare and Web3.

  • How often is the blog updated?

    Pharos Production publishes new articles regularly based on industry developments, project learnings and technology releases. Each article goes through technical review and fact-checking before publication.

    Subscribe or check back for the latest insights on software development.

  • Can I reference blog articles in my project research?

    Yes. All articles on the Pharos Production blog are freely accessible and may be cited with attribution. For deeper technical consultation or custom research on a topic covered in our articles, contact our engineering team directly.

Last reviewed:

Last updated:

Dmytro Nasyrov, Founder and CTO at Pharos Production
Dmytro Nasyrov Founder & CTO Let's work together!

Your business results matter

Achieve them with minimized risk through our bespoke innovation capabilities

Your contact details
Please enter your name
Please enter a valid email address
Please enter your message

We use your details only to reply to your request. Data Privacy and Legal Notice

We typically reply within 24 hours

What happens next?

  1. Contact us

    Contact us today to discuss your project. We're ready to review your request promptly and guide you on the best next steps for collaboration

    Same day
  2. NDA

    We're committed to keeping your information confidential, so we'll sign a Non-Disclosure Agreement

    1 day
  3. Plan the Goals

    After we chat about your goals and needs, we'll craft a comprehensive proposal detailing the project scope, team, timeline and budget

    3-5 days
  4. Finalize the Details

    Let's connect on Google Meet to go through the proposal and confirm all the details together!

    1-2 days
  5. Sign the Contract

    As soon as the contract is signed, our dedicated team will jump into action on your project!

    Same day