Skip to content

Last updated

Engineering

  • A compliance officer laying a thin national registration certificate beside a thick authorization decision on a desk, comparing two crypto authorization regimes against a hand ruled decision table
    CASP vs VASP

    VASP is a supervisory label that appears nowhere in EU legislation, used by national regulators for firms on the anti-money-laundering registers the Fifth Anti-Money Laundering Directive required. CASP is an authorization under MiCA Title V with a defined service list and an EU passport. This guide sets the entity-level regimes side by side, including the electronic money institution license and the Article 60 notification route that removes the need for a CASP application for seven categories of already-licensed institution.
  • Close up of a secure door in a custody operations room with an access reader, a hand filled access log on a clipboard and a sealed cabinet for crypto-asset safekeeping.
    MiCA Custody Requirements

    MiCA custody requirements mapped provision by provision: Article 70's safekeeping baseline for every CASP, Article 75's nine-paragraph custody rulebook, the three-limb segregation test, the liability cap at market value at time of loss and the evidence a CASP should have ready for each obligation.

  • Two distribution engineers laying out printed message sample sheets in sequence across a long desk, the Offer to Order message flow behind an airline NDC integration
    NDC API Integration

    NDC API integration for a flight-booking platform: the Offer and Order message set message by message, aggregator versus direct connect, servicing after the sale and what IATA's own capability program actually measures.

  • Printed export inventory on a desk, permission lists beside a schema diagram, a catalog table and a network trust diagram
    Data Act cloud switching requirements

    Article 30 of the EU Data Act splits a switching duty by capability, not by service-model label, and Article 2(37) defines functional equivalence in law while no published standard operationalises it into a threshold. This article works through the exemption gate, the export inventory beyond raw data and the escrow-and-rebuild record that stands in for the missing standard, including the correction most coverage misses: 12 January 2027 zeroes switching charges, not multi-cloud egress.

  • Two records of the same fund holdings compared side by side, a printed ledger listing and a bound shareholder register
    Tokenized fund register reconciliation

    A tokenized fund runs two books, the ledger the token moves on and the shareholder register a transfer agent maintains, and three published regimes now say which one wins when they disagree, in two opposite directions. None of them says how anyone learns the two diverged, at what cadence or where the investor stands between a bad entry and its reversal.

  • An on-duty engineer standing at a desk with a phone handset lifted off its cradle and starting the first entry on a blank printed incident record form, the moment one of the AI Act reporting clocks starts running
    AI Act Serious Incident Reporting

    The AI Act defines a serious incident in four alternative limbs and attaches three different reporting deadlines to them, and since 27 July 2026 the recipient of the report depends on who supervises the provider.

  • Two bound hardcover incident logbooks lying open side by side on one desk with visibly different column rulings and a separate pen resting in each, the two independent classification passes a financial entity runs under the AI Act and DORA
    AI Act and DORA Overlap

    How the EU AI Act and DORA land on the same financial entity without either text citing the other, why Article 74(6) puts the AI file on the financial supervisor's desk, and what Articles 26(5), 26(6), 72(4) and 73(9) actually change.

  • A bank compliance officer reading from an open supplier manual while a colleague fills a single row on a wide ruled sheet whose other rows stay empty, the deployer side fundamental rights impact assessment owed by banks and insurers under the AI Act
    AI Act Fundamental Rights Impact Assessment

    Article 27 of the AI Act puts the fundamental rights impact assessment on the deployer, names creditworthiness and life and health insurance pricing explicitly, and since July 2026 lets it cross-reference an existing data protection impact assessment.

  • A hand-ruled monitoring plan draft on plain paper beside a printed list of logging fields on a working desk, the Article 72 plan a team has to design itself because the mandatory template never issued
    AI Act Post-Market Monitoring Plan

    What Article 72 of the EU AI Act requires of a post-market monitoring system and plan, why the mandatory Commission template was repealed before it ever appeared, and what telemetry, logging and retention an engineering team has to build to make the plan real.

  • A provider's own staff signing the declaration page on a thick conformity file in a small office with no external assessor present, the Annex VI internal control route for credit scoring and insurance pricing under the AI Act
    AI Act Conformity Assessment

    Which conformity assessment procedure applies to a high-risk AI system under Article 43, why Annex III point 5 credit and insurance systems take the Annex VI internal control route with no notified body involved, and what evidence a self-assessment has to produce and keep.

  • Macro of a printed source document marked with cut lines at its section breaks and one exception clause bracketed back to the rule above it.
    RAG Data Pipeline

    A RAG corpus is a live system with state, not a build artifact. This piece traces one document through arrival, change, duplication, deletion and embedding model migration, and shows where five major vector stores document contradictory answers to the same event.

  • Three colleagues laying out a dated compliance sequence along a long paper wall planner and moving small cards between three separate dated windows, the timeline work behind EU AI Act compliance
    EU AI Act Compliance

    A dated EU AI Act compliance timeline and applicability map after Regulation (EU) 2026/1744, covering what changed in Article 113, Article 6 and Article 50 and why EUR-Lex, the Commission's AI Act tool and the most-cited third-party tracker still show the pre-amendment rules.

  • Five national application dossiers of visibly different thickness laid in a row beside a desk calculator and a printed fee schedule, the cost of a MiCA CASP licence across Member States
    CASP License Cost by Country

    CASP license cost broken down per EU country: national regulator fees from Latvia's EUR 2,500 to Malta's EUR 25,000, MiCA's EU-wide capital floors, market total-setup estimates, the Poland no-license-window trap and passporting under Article 65.

  • Close up of a printed payment provider shortlist with four entries circled and one crossed out, on a treasury desk beside a monitor edge and a card terminal.
    Stablecoin Payment API Selection: Orchestration vs Issuance

    Stablecoin payment API selection for CTOs and engineering leads: orchestration vs issuance API compared, a six-provider landscape table and the custody, licensing and off-ramp criteria that actually decide the pick.

  • Two clipped printed legislative texts on a payments engineering desk under a magnetic wall planner strip whose first slot sits empty, PSD3 and PSR planning without a publication date
    PSD3 Compliance Requirements

    PSD3 and PSR compliance is an offset from an unset anchor, not a calendar date. The 21 and 27 month tiers, sourced from the Council's April 2026 compromise texts, and what a build has to have ready before either clock starts.

  • Duty analysts at a public sector security operations desk during a shift handover with a wall clock and a paper incident log between them.
    NIS2 Compliance Software Requirements

    NIS2 never names a software company as a regulated type. This piece sorts a software vendor into the route that actually applies, then lists the artifacts each route asks it to keep on a shelf.

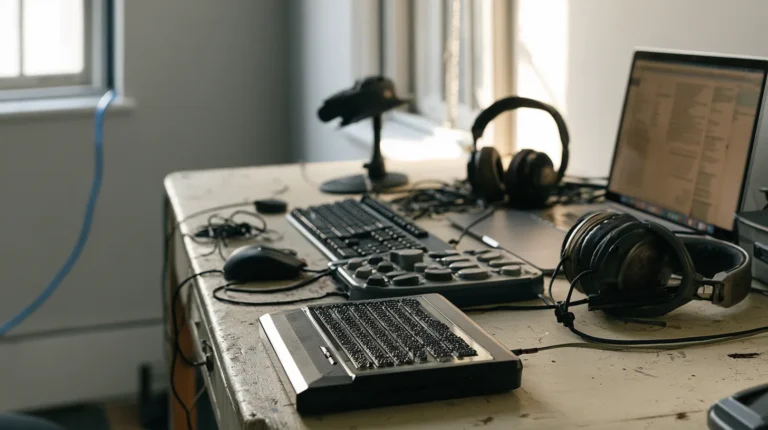
  • An accessibility testing bench laid out with a refreshable braille display, a keyboard with the mouse set aside, a switch access pad and headphones.
    European Accessibility Act Compliance

    The European Accessibility Act never names WCAG or EN 301 549. This piece sorts a software company into the role that actually carries liability, and states plainly why the standard everyone cites carries no legal presumption here.

  • A printed identity intake form with five filled rows and a run of blank rows beneath them, one filled row marked with a small paper flag, standing in for the five guaranteed EUDI Wallet identity fields against fourteen optional fields that may never arrive
    EUDI Wallet Onboarding

    Person identification data guarantees five fields and marks fourteen more optional, and a mandatory field may carry a substituted value where the real one is unknown. What an onboarding flow can and cannot assume from a wallet presentation.

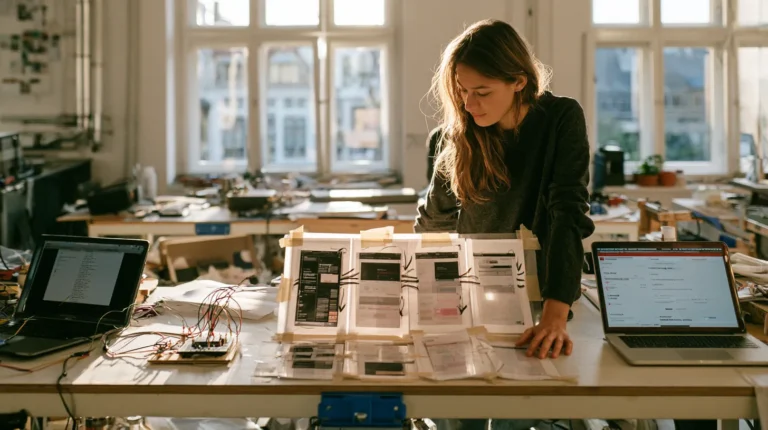
  • Engineer at a prototype bench between a wired test rig, a taped row of printed paper screen mockups and a laptop showing a working sign up form, proof of concept and prototype and MVP deliverables
    PoC vs MVP vs Prototype

    PoC vs MVP vs prototype explained as three different questions rather than three sizes of the same build, with real cost ranges and a decision framework for which to build first.

  • Close up of a printed two column triage sheet and a fanned stack of index cards on a security operations desk with wall monitors behind.
    CRA Severe Incident Classification

    The Cyber Resilience Act never defines severe as a standalone term. The threshold sits in Article 14(5), narrowing the general incident definition to sensitive or important data or functions, or to malicious code, while Article 3(42) sets a separate evidentiary bar for actively exploited that a high severity score alone does not meet.

  • A thick ring binder with archive tabs beside a slim saddle stitched booklet on a table, each with its own addressed envelope, the split between the two audiences a general-purpose AI model provider must write for
    GPAI Model Obligations

    What a general-purpose AI model provider owes regulators under Annex XI versus downstream integrators under Annex XII, where the open-source carve-out stops and why GPAI penalties sit in Article 101, not Article 99.

  • Printed routing directory pages spread across a table with one entry tabbed and a magnifier resting on it beside a mechanical stopwatch, the lookup and the fixed clock in a Verification of Payee build
    Verification of Payee Implementation

    Verification of Payee is two jobs in one build, and the scheme treats them very differently. The requesting side is a specified round trip with a five second envelope and a discard rule. The responding side is a specified message shape wrapped around a decision the scheme declines to make, in a guidance document that says it is not part of the Rulebook and that the responder is free to ignore. This walks the message lifecycle position by position, states each one twice and closes each one on the contract both sides owe.

  • Overhead view of an open printed regulation volume with colour coded tabs beside two columns of handwritten index cards joined by pencil arrows
    RWA Compliance Controls: Mapping Regulations to Smart Contracts

    RWA compliance controls mapped duty by duty to the specific smart-contract mechanism that enforces it, from ONCHAINID identity registries and jurisdiction gates to Rule 144 lockups, investor caps, sanctions screening and forced transfer, plus the MiFID II vs MiCA boundary that decides which EU rulebook applies.

  • A printed product feature list annotated down a five step sequence with index tabs and two small product photographs clipped beside it, the high-risk classification test under the EU AI Act
    AI Act High Risk Classification

    How to classify an AI system as high-risk under Article 6 and Annex III of the EU AI Act after the Digital Omnibus, with the new 1a to 1c carve-outs, a decision tree and worked examples.

  • Five vendor pricing sheets fanned in a row on a desk beside a handwritten notepad of measured trace usage, the working papers behind an LLM observability cost comparison
    LLM Observability Cost

    A real LLM observability cost model built from verified vendor pricing retrieved 2026-08-08, showing why Langfuse, LangSmith, Braintrust and Arize cannot be compared on list price alone and how the OpenTelemetry GenAI conventions' Development status quietly breaks naive cost attribution.

  • A payments operations analyst standing at her desk checking a printed batch of customer payment records against a screen in a bank operations room before the ISO 20022 address deadline.
    ISO 20022 Structured Address Migration: What Breaks on 15 November 2026

    The EPC's 15 November 2026 inter-PSP settlement date and Swift's 14 November 2026 SR 2026 go-live are two different events on one cutover weekend. This walks an address population through seven gates, from scope to the inter-PSP double rejection duty, and states at each gate which records die and what the remedy is.

  • Two reviewers checking printed disclosure icon proofs against printed video frame stills on a long review bench, the marking check required by AI Act Article 50
    AI Act Article 50

    What Article 50 of the EU AI Act actually requires for marking AI-generated content, the two mandatory layers, the transitional date hidden in Article 111(4) and the failure modes the Code of Practice admits marking cannot survive.

  • Hands and shoulders of two colleagues comparing clauses across three thick ring binders opened flat in a small meeting booth.
    CRA NIS2 and DORA Reporting Overlap

    A company that is at once a CRA manufacturer, a NIS2 essential or important entity and a DORA financial entity keeps three separate reporting duties on three separate filings, even where two of them reach the same national CSIRT. The CRA's Single Reporting Platform consolidates filings within the CRA itself and does not fold NIS2 or DORA into that filing.

  • Two colleagues in a documentation and print room, one lifting a printed checklist from an office printer while the other types into a plain web form on a laptop.
    CRA Single Reporting Platform Integration

    The CRA's Single Reporting Platform is a web form and case management system that ENISA runs, not an API, with no published roadmap for one. Registration runs through named individual Assigned Representatives, and one notification record moves through three stages that lock for good once the final report is submitted.

  • An auditor's reserve file open at a tabbed valuation section on a desk beside a sealed filing envelope and a desk calendar, the six-monthly attestation evidence behind electronic money token issuance
    Electronic Money Token Issuance

    MiCA describes an accounting outcome for an e-money token and almost never a mechanism. This follows one euro through the licence gate, the mint, placement, circulation, the redemption request, burn and attestation, states which of those steps the Regulation actually specifies and names the two places where it specifies nothing at all.

Dmytro Nasyrov, Founder and CTO at Pharos Production
Dmytro Nasyrov Founder & CTO Let's work together!

Your business results matter

Achieve them with minimized risk through our bespoke innovation capabilities

Your contact details
Please enter your name
Please enter a valid email address
Please enter your message

We use your details only to reply to your request. Data Privacy and Legal Notice

We typically reply within 24 hours

What happens next?

  1. Contact us

    Contact us today to discuss your project. We're ready to review your request promptly and guide you on the best next steps for collaboration

    Same day
  2. NDA

    We're committed to keeping your information confidential, so we'll sign a Non-Disclosure Agreement

    1 day
  3. Plan the Goals

    After we chat about your goals and needs, we'll craft a comprehensive proposal detailing the project scope, team, timeline and budget

    3-5 days
  4. Finalize the Details

    Let's connect on Google Meet to go through the proposal and confirm all the details together!

    1-2 days
  5. Sign the Contract

    As soon as the contract is signed, our dedicated team will jump into action on your project!

    Same day