Pharos Production has partnered with Pleenk to build a secure, scalable payments platform for fast transactions, fraud prevention and seamless integration with digital products. The platform processes payment flows in real time while maintaining high levels of security, transparency and reliability for both businesses and end users. Built on cloud-native infrastructure and an event-driven architecture, Pleenk provides a strong foundation for modern digital payments.
Last reviewed August 15, 2026
AI Governance Consulting
Pharos Production provides AI Governance consulting services that help organizations deploy artificial intelligence responsibly, transparently and in compliance with evolving regulations.
- 25+ AI projects delivered
- 90+ engineers
- 108 Clutch reviews
282 published client reviews across 3 platforms. Counts are summed; reviewers may appear in more than one source.
Profiles checked . Glassdoor: 46 employee reviews, 5.0/5, reported separately.
Case Study
See the products we built and the engineering work involved. Each case describes its scope and delivery context.
-
-
Pharos Production partnered with Nextcheck to replace outdated, manual onboarding with a secure, automated KYC/AML platform. Built on AWS, Kubernetes, Istio, Elixir, RabbitMQ, PostgreSQL and NextJS, the platform provides real-time biometric and document verification, risk assessment and compliance reporting. Since 2019, Nextcheck has reduced onboarding time by 60%, cut manual labor by 70% and expanded to support thousands of checks at once. Today, it powers global banks, FinTechs and crypto firms with a cloud-native, regulation-ready, growth-oriented compliance platform.
-
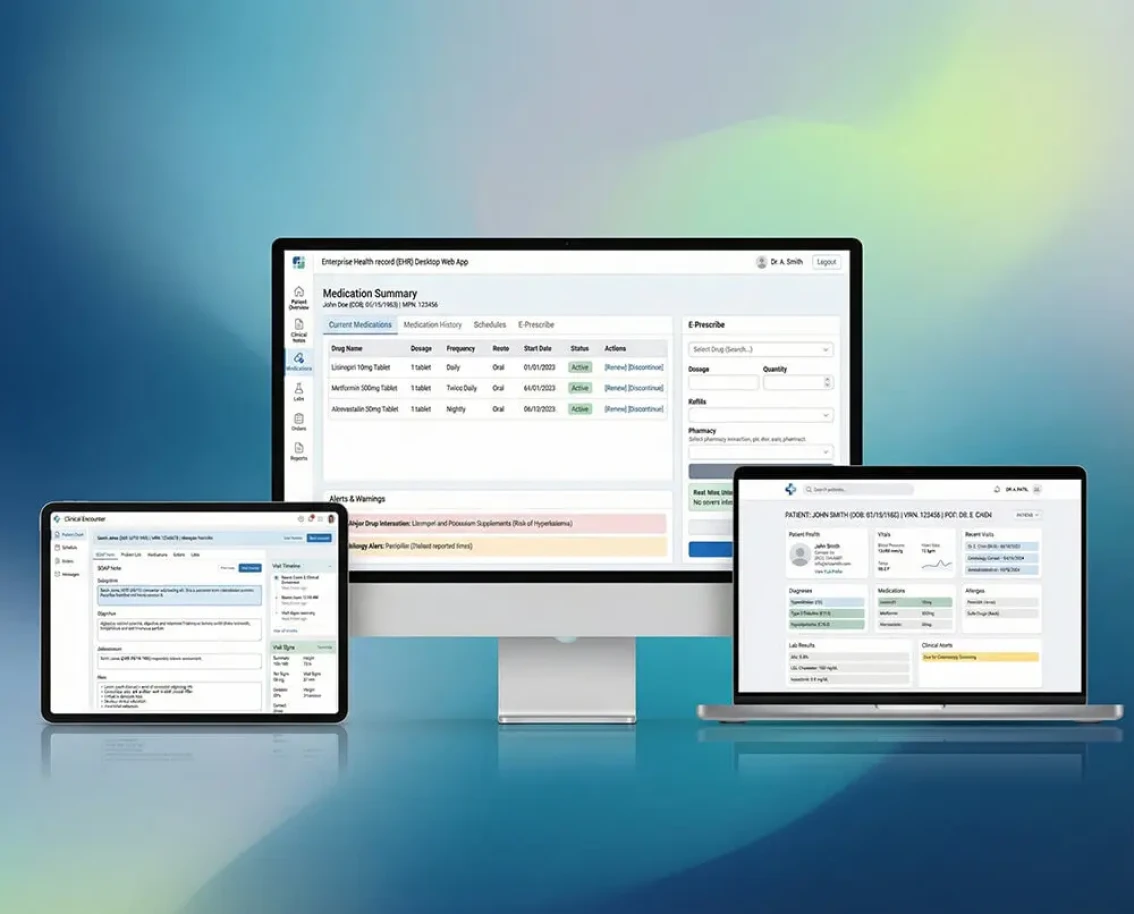
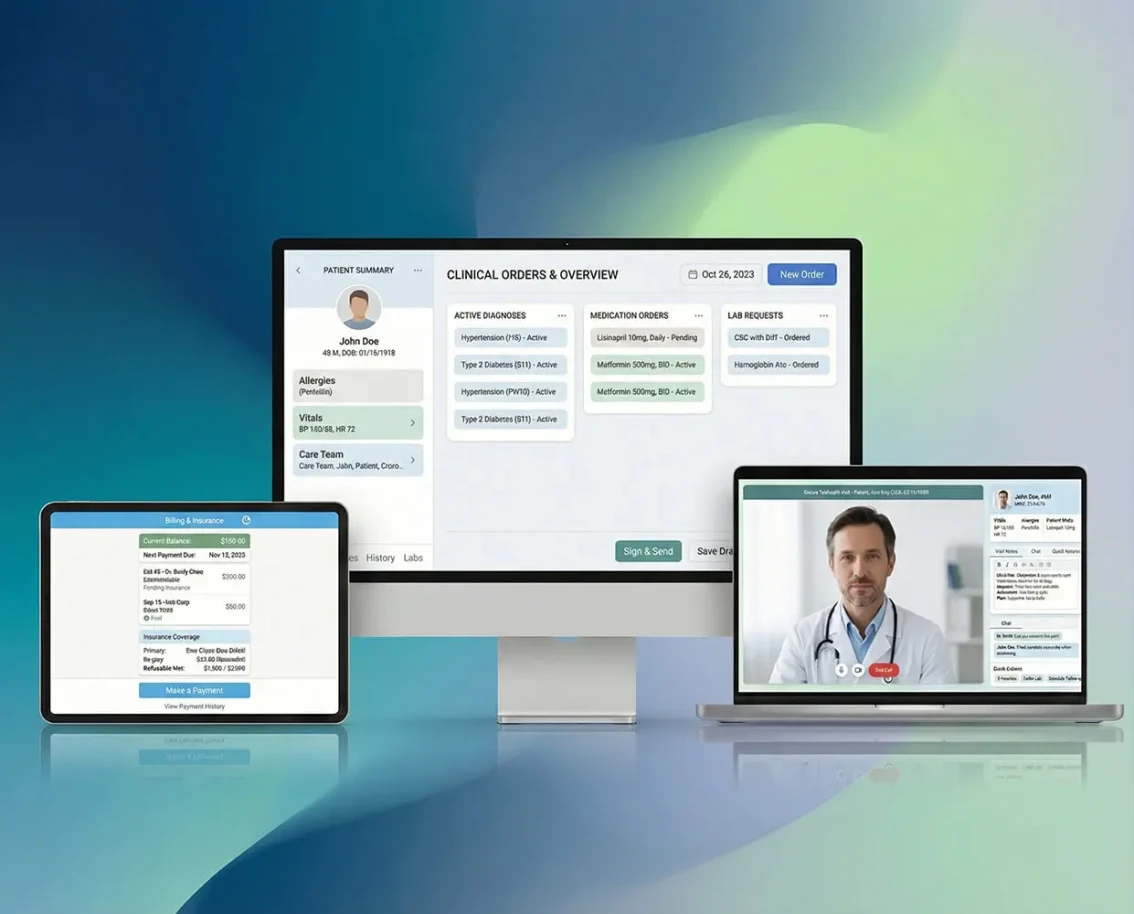
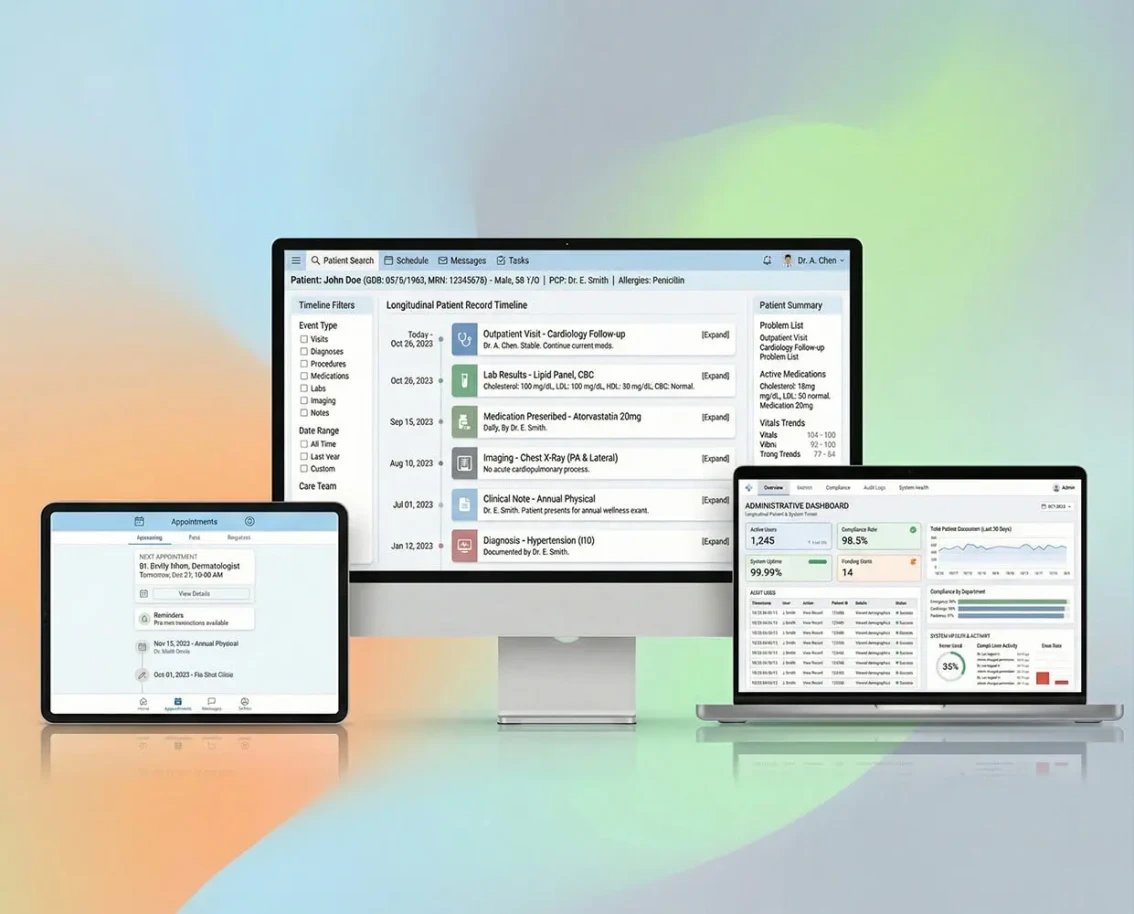
Pharos Production partnered with a healthcare organization to design and build MedCore, a comprehensive electronic health record platform that centralizes patient data, streamlines clinical workflows and ensures regulatory compliance. The system unifies medical records, clinical documentation, diagnostics and administrative processes within a secure, scalable digital environment. Built on a cloud-native architecture, MedCore delivers reliable performance, real-time data access and long-term scalability for healthcare providers operating at clinic, hospital and network levels.
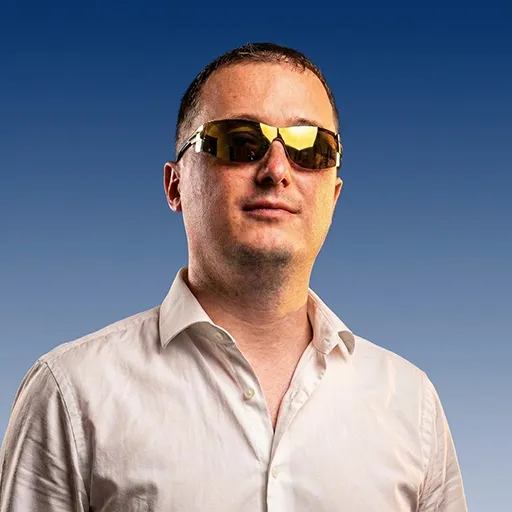
Practice led by Dmytro Nasyrov
Founder and CTO
23+ years in custom software development. Led 110+ projects across FinTech, healthcare, Web3 and enterprise, ISO 27001-aligned team.
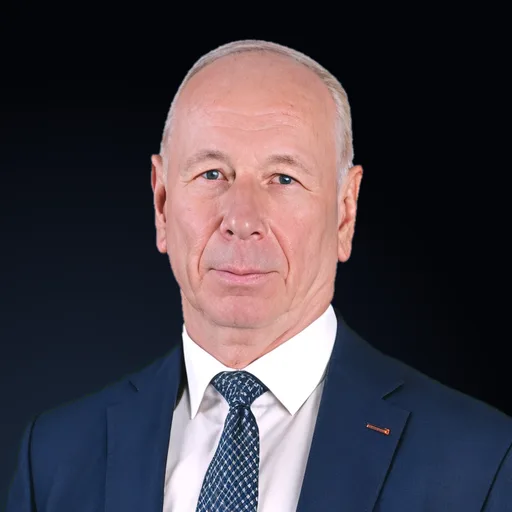
Technically reviewed by Victor Sineglazov, D.Sc.
Independent AI Scientific Advisor
Professor, Artificial Intelligence Department, Igor Sikorsky Kyiv Polytechnic Institute. Head of the Aviation Computer-Integrated Complexes Department, Kyiv Aviation Institute.
Reviewed for technical accuracy on August 15, 2026. Not an endorsement of any commercial claim on this page.
What is AI governance?
Authoritative citations 12 sources
-
Stanford AI Index
The Stanford AI Index tracks multi-year movement on ML benchmarks, training compute, responsible AI metrics and enterprise adoption across industries, making it the most cited yearly reference for grounding ML investment cases.
hai.stanford.edu
-
Papers With Code
Papers With Code maintains live state-of-the-art leaderboards for ML tasks across image classification, object detection, NLP and tabular prediction, which we use to pick baselines before committing to a model family.
paperswithcode.com
-
arXiv, Chen and Guestrin 2016
The XGBoost paper by Chen and Guestrin remains the most cited gradient boosting reference and underpins tabular ML baselines we still ship in FinTech and logistics systems a decade after publication.
arxiv.org
-
NeurIPS 2017, LightGBM
Ke et al. introduce Gradient-based One-Side Sampling (GOSS) and Exclusive Feature Bundling (EFB) in LightGBM. Their experiments compare efficiency on the datasets in the paper; production performance depends on the workload.
proceedings.neurips.cc 2017
-
McKinsey State of AI
McKinsey documents annual enterprise ML adoption across functions like marketing, service operations and supply chain, and consistently reports that scaled ML correlates with higher EBIT contribution versus pilot-only organizations.
mckinsey.com
-
Gartner AI Hype Cycle
Gartner maps enterprise ML techniques across the hype cycle phases, flagging which capabilities are production-ready for mid-market adoption versus still speculative, which we cross-check before recommending a build path.
gartner.com
-
IDC Worldwide AI Spending Guide
IDC publishes the worldwide AI spending guide with multi-year forecasts by industry, use case and geography, which we reference when sizing three-year total cost of ownership for ML platform engagements.
idc.com
-
NIST AI Risk Management Framework
The NIST AI RMF defines a govern, map, measure and manage lifecycle for AI systems that we apply to production ML including model cards, bias testing and incident response procedures for regulated deployments.
nist.gov
-
OWASP ML Security Top 10
OWASP maintains a ranked list of the top machine learning security risks including input manipulation, training data poisoning, model theft and adversarial attacks, which we use as a threat model checklist before exposing any ML endpoint.
owasp.org
-
O'Reilly AI Adoption in the Enterprise
The O'Reilly AI adoption survey tracks ML maturity stages across enterprises, reporting on deployment percentages, skills gaps and the most common production blockers which consistently include data quality and monitoring rather than model choice.
oreilly.com 2022
-
Google Cloud MLOps Architecture
Google Research published the canonical MLOps continuous delivery reference describing three maturity levels from manual to fully automated pipelines, which we use as the template for client MLOps roadmaps and capability gap assessments.
cloud.google.com
-
PyTorch Blog
The PyTorch engineering blog tracks the 2.x production tooling surface including torch.compile, TorchServe updates and quantization workflows, which shape our default serving stack for sub-50ms p99 inference on GPU and CPU targets.
pytorch.org
- Governance as PowerPoint (we decline compliance-theater engagements)
- AI governance without engineering implementation capacity
- Projects where leadership will not commit to the control framework
- One-time audits with no ongoing monitoring plan
AI governance at Pharos Production at a glance
- Governance engagements: 6+ governance engagements since 2023 across finance, healthcare, insurance, regulated SaaS
- Frameworks: EU AI Act, NIST AI RMF, ISO 42001, OCC model risk management, state-level AI laws
- Controls: Model cards, data lineage, bias testing, audit logging, explainability, human-in-the-loop, incident response
- Pricing: Governance assessment from $20,000; full implementation $60,000-$250,000+; retainers from $8,000/month
- Timeline: Assessment 3-5 weeks; implementation 3-6 months; quarterly ongoing reviews
- Legal boundary: Pharos implements controls; clients engage qualified counsel on legal interpretation of frameworks
- Honest scope: We decline compliance-theater engagements and PowerPoint-only governance work
Our AI governance framework
Governance engagements follow a phased approach: discovery maps AI systems and risk categories; build implements controls (model cards, data lineage, audit logs, bias testing); production readiness delivers the first governance board review; support includes quarterly control audits and regulatory change monitoring.
-
Phase 01 / 04 Paid Discovery
Week 0
2-4 weeks
- Technical validation
- Architecture proposal
- Scope refined estimate
82% on-schedule with discovery
-
Phase 02 / 04 Iterative Build
Week 2-4
2-week sprints
- Working demos every sprint
- CTO review at milestones
- ADRs documented
Transparent progress tracking
-
Phase 03 / 04 Production Readiness
Week 8-24
- Monitoring and alerting
- Security audit Pen test
- Runbooks and rollback
ISO 27001 aligned
-
Phase 04 / 04 Support
Launch day
Ongoing
In progress
- Security patches
- Performance tuning
- 4h SLA response
Continuous improvement
Pharos Verified Delivery applied to 110+ production applications since 2013
Governance engagements we ran
Three AI governance engagements across regulated industries. Each surfaced a different control gap during the review.
EU AI Act readiness
Underwriting model deployed without formal documentation. EU AI Act high-risk classification triggered documentation requirements the client could not produce in a week.
Model cards, data lineage, bias testing and human-review flow documented to the regulator's satisfaction. Classified as compliant in the first review round. Governance board established for ongoing AI oversight.
We worked backwards from the EU AI Act Article 13 transparency requirements. Every existing deployment got a model card with the same structure; new deployments are blocked until the model card exists.
Healthcare AI controls
Clinical support model deployed with no bias testing across demographics. Client health system raised equity concerns before going live.
Bias testing across 9 demographic slices, with documentation of any disparity above 5%. Two disparities surfaced and corrected before production. HIPAA-compatible audit logging deployed across all model inference calls.
The bias testing is not a one-off - it runs nightly against a fixed demographic test set. Any disparity above threshold pages the governance board automatically.
Financial services model risk
Fraud detection model in production for 3 years with no model risk management (MRM) documentation. OCC examiner flagged the gap.
Full MRM package: model development documentation, validation report, ongoing monitoring plan, change management. OCC examiner cleared the finding at the next visit. Process now scales to new models.
MRM documentation was the deliverable; the process to produce it for future models was the real work. We built a template that the bank's model developers fill in at build time, not after regulators ask.
Client names anonymized under NDA. Full case studies at /cases/.
When governance projects go wrong
We decline roughly 30% of RFPs we receive. Forcing a bad fit costs both sides 3-6 months and damages outcomes. Here is how we think about scope:
- Governance as PowerPoint without engineering implementation
- Projects without commitment from compliance and engineering leadership
- Governance requests triggered by regulator notice rather than proactive risk awareness
- Frameworks adopted without tailoring to the specific AI systems
- One-time audits with no ongoing monitoring plan
Governance work that stops at policy documents fails during the first real incident. Effective governance means the controls are implemented in code - automated bias testing, audit logs on every inference, model cards generated from CI, explainability surfaced in the product UI. PowerPoint governance is theater; implementation-led governance is the actual work.
Regulatory and framework reading
State of AI Development Costs 2026 AI cost and governance economics based on Pharos delivery data. Continue readingPharos AI governance portfolio
Pharos AI governance delivery portfolio observations, 2021-2026
Ranges we consistently see across 30+ governance engagements.
-
Typical 5 business days for risk classification, 3-4 weeks for first full documentation set (model card, datasheet, runbook).
-
Approximately 35-50% of engagements involve high-risk AI systems requiring full EU AI Act documentation scope[5].
-
Approximately 20-35% of reviewed models have at least one statistically meaningful subgroup disparity requiring mitigation or documented accept-with-disclosure.
-
Typical 10-30 business days from governance package delivery to procurement acceptance; faster than starting documentation from scratch at the procurement gate.
-
60-80% of clients retain us for quarterly governance reviews, incident response and regulation delta propagation post-baseline delivery.
AI governance consulting outlook 2026-2027
Three shifts are reshaping AI governance engagements.
-
EU AI Act enforcement makes documentation mandatory
High-risk AI system classification, model cards and incident response procedures become binding EU regulation. Organizations without documentation processes cannot deploy regulated AI systems in EU markets[8].
-
Model cards and bias audits enter procurement requirements
Enterprise buyers require published model evaluation, bias testing and datasheet artifacts as contract deliverables. Vendors without structured governance documentation fail procurement review[6].
-
AI incident response inherits cybersecurity patterns
AI incident runbooks, rollback procedures and post-mortem discipline adopt patterns from cybersecurity incident response. Organizations without structured AI incident response accumulate silent failures[9].
Our four-dimension AI governance evaluation template
Every AI governance engagement we ship runs against the same four-dimension readiness evaluation before handover.
-
30%
Risk classification
NIST AI RMF levels mapped to system, legal jurisdiction
NIST AI RMF govern, map, measure, manage lifecycle applied; risk level documented per system; jurisdiction-specific overlays (EU AI Act, US executive order) mapped[8].
-
25%
Documentation completeness
Model cards, datasheets, incident runbooks
Model cards published per production model; training data datasheets documented; incident runbook with rollback procedures and notification obligations[6].
-
25%
Bias and fairness testing
Protected attribute evaluation, subgroup performance
Protected-attribute subgroup performance evaluated on holdout; disparity thresholds documented; remediation or accept-with-disclosure path defined[9].
-
20%
Audit trail
Decision logging, human override, review cadence
Every model decision logged with input hash and version; human override pathway documented; quarterly governance review cadence scheduled[10].
Production post-mortem
When high-risk classification unblocked a blocked procurement cycle
A healthcare AI client engaged us in Q1 2025 for a governance review of a clinical decision-support model. Procurement had stalled because no structured classification existed. Our four-week review classified the system as high-risk under EU AI Act scope, produced a model card, documented bias testing results and published an incident runbook. The procurement team accepted the package in under 10 business days.
Governance baseline now leads with risk classification before model documentation, because classification determines which documentation is mandatory versus optional. Standard engagement scope includes 5 business day classification plus 3-4 weeks of documentation work.
Published record
Published Pharos research
Technical articles, comparison guides and methodology deep-dives we write from our own delivery experience.
- State of AI Development Costs 2026
- AI Agent Frameworks Comparison 2026
- Build vs Buy AI Agent: 2026 Decision Framework
- RAG vs Fine-Tuning: When to Use Each Approach
- How to Choose an AI Development Company
- State of Smart Contract Audits 2026
- State of Production AI Engineering 2026
- State of FinTech Compliance Cost 2026
- State of Custom Software TCO 2026
- State of AppSec 2026
- State of Tech Due Diligence 2026
- State of QA and Software Testing 2026
- State of DevOps and Cloud 2026
- How to Choose a Blockchain Development Company
- How to Choose a FinTech Development Company
- FinTech Compliance Checklist 2026: PCI DSS, SOC 2, GDPR and Beyond
- AI in FinTech: Transforming Financial Services in 2026
- Software Development Cost Guide: What to Expect in 2026
- How to Choose a Software Development Company in 2026
- Cybersecurity Essentials for Startups and SMBs in 2026
- FinTech Trends 2026: How Top FinTech Trends are Shaping Digital Banking
Platforms we work with
Technology platforms and company references shown for identification. A logo does not establish a commercial partnership or endorsement.
16 references-
Consensys
-
Gate.io
-
Coinbase
-
Ludo
-
Core Scientific
-
Debut Infotech
-
Axoni
-
Alchemy
-
StarkWare
-
MARA Holdings
-
MicroStrategy
-
Nubank
-
OKX
-
Uniswap
-
Riot
-
LeewayHertz
About the founder and CTO
Founder and CTO Pharos Production
I design and build reliable software solutions - from lightweight apps to high-load distributed systems and blockchain platforms.
PhD in Artificial Intelligence, MSc in Computer Science (with honors), MSc in Electronics & Precision Mechanics.
-
13 years in architecture of great software solutions tailored to customer needs for startups and enterprises
-
23 years of practical enterprise customized software production experience
-
Lecturer at the National Kyiv Polytechnic University
-
Doctor of Philosophy in Artificial Intelligence
-
Master's degree in Computer Science, completed with excellence
-
Master's degree in Electronics and precision mechanics engineering
Choose your project scope
Pharos Production scopes engagements in three tiers, Proof of concept, MVP build and Enterprise platform, with typical budgets from $10,000 to $500,000+ depending on scope and complexity.
Proof of concept
Focused validation of your riskiest technical assumption with a working spike and a clear build-or-pivot recommendation.
MVP build
Production-ready first version with core flows, real backend and the integrations to onboard first paying users.
Enterprise platform
Full-scale build with architecture, DevOps, QA, security and long-term evolution.
Prices vary based on project scope, complexity, timeline and requirements. Hourly rates range from $50 to $99 depending on role and seniority. Contact us for a personalized estimate.
Interaction models for staff augmentation, dedicated teams and outsourcing
Request staff augmentation
Need extra hands on your software project? Our developers can jump in at any stage - from architecture to auditing - and integrate seamlessly with your team to fill any technical gaps.
Hire dedicated experts
Whether you're building from scratch or scaling fast, our engineers are ready to step in. You stay in control, and we handle the code.
Outsource your project
From first line to final audit, we handle the entire development process. We will deliver secure, production-ready software, while you can focus on your business.
Technologies, tools and frameworks we use
We select the stack for your product, integrations and operating requirements.
AI and Machine Learning
LLM Providers 8
AI Frameworks 15
Vector Databases 7
MLOps and Infrastructure 11
AI Agent Tools 4
Partnerships and awards
Selected badges from Clutch, GoodFirms and The Manifest. Open the issuer profiles to review categories and dates.
An approach to the development cycle
-
Team Assembly
Our company starts and assembles an entire project specialists with the perfect blend of skills and experience to start the work.
-
MVP
We'll design, build and launch your MVP, ensuring it meets the core requirements of your software solution.
-
Production
We'll create a complete software solution that is custom-made to meet your exact specifications.
-
Continuous Support
Our company will be right there with you, keeping your software solution running smoothly, fixing issues and rolling out updates.
AI governance insights
AI governance glossary 7
- EU AI Act
- EU regulation effective 2024 that classifies AI systems into risk tiers (unacceptable, high, limited, minimal) and imposes conformity assessment, transparency and post-market monitoring obligations on developers and deployers.
- NIST AI RMF
- A voluntary US framework published by NIST in 2023 that structures AI risk management across four functions - Govern, Map, Measure and Manage - to improve trustworthiness of AI systems.
- Model Risk Management (MRM)
- A discipline originating in financial regulation (SR 11-7) that requires organizations to validate, monitor and control risks arising from models used in decision-making, now expanding to AI systems broadly.
- Explainable AI (XAI)
- A set of methods and tools - SHAP, LIME, counterfactuals - that make machine learning model predictions interpretable to human stakeholders, supporting regulatory compliance and internal audit requirements.
- ISO/IEC 42001
- The international standard specifying requirements for establishing, implementing and continually improving an artificial intelligence management system within an organization.
- Differential Privacy
- A mathematical technique that adds calibrated statistical noise to datasets or query results to protect individual-level information while preserving aggregate analytical utility in AI training pipelines.
- Demographic Parity
- A fairness metric requiring that a model's positive prediction rate is equal across demographic groups, used to detect discriminatory outcomes in classification systems such as credit scoring or hiring tools.
Frequently asked questions about AI Governance Consulting
Type to filter questions and answers. Use Topic to narrow the list.
Showing all 9
No matches
Try a different keyword, change the topic or clear filters
-
What does an AI governance framework actually include?
An AI governance framework covers the policies, roles, controls and technical measures that manage AI risk across a model's full lifecycle - from data sourcing and training through deployment, monitoring and retirement. It defines who approves model changes, how bias is measured, what audit trails are maintained and how the organization demonstrates compliance to regulators or auditors.
-
Which regulations and standards does Pharos align governance work to?
Engagements map to the EU AI Act (risk tiers, conformity assessments and post-market monitoring obligations), NIST AI RMF (Govern, Map, Measure and Manage functions), ISO/IEC 42001 (AI management system standard) and sector-specific overlays including HIPAA for health AI and SR 11-7 / SS1/23 for financial model risk management.
-
How is AI model bias detected and documented?
Bias detection applies statistical fairness metrics - demographic parity, equalized odds and calibration - across protected attribute groups defined by your jurisdiction. Pharos builds automated bias evaluation pipelines that run on each model version and produce structured reports suitable for internal review boards and regulatory submissions.
-
What is explainability (XAI) and when is it legally required?
Explainability techniques - SHAP, LIME, attention visualization and counterfactual explanations - make a model's predictions interpretable to human reviewers. The EU AI Act requires explanations for high-risk AI decisions affecting individuals (credit, hiring, medical diagnosis). GDPR Article 22 grants individuals the right to a meaningful explanation of automated decisions.
-
How do you handle data privacy within AI model training and inference?
Data privacy controls span pseudonymization and anonymization of training sets, differential privacy for sensitive datasets, data minimization reviews to remove unnecessary PII and contractual data processing agreements with model API providers. For inference, PII detection layers can redact sensitive fields before data reaches a third-party model endpoint.
-
What does a model audit trail capture and how long must records be kept?
Audit trails record model version, training data lineage, evaluation metrics at release, changes to prompts or hyperparameters, production inference logs and human override events. Retention periods depend on regulation - the EU AI Act mandates at least 10 years for high-risk systems; financial sector requirements typically follow SR 11-7 model inventory rules.
-
How long does a typical AI governance engagement take?
A focused gap assessment against NIST AI RMF or EU AI Act takes 4 to 6 weeks and delivers a prioritized remediation roadmap. Full framework implementation - policy authoring, tooling integration, staff training and audit-ready documentation - typically runs 12 to 20 weeks depending on the number of models in scope and existing data governance maturity.
-
When does Pharos decline?
We decline compliance-theater engagements, governance without engineering implementation capacity, projects without leadership commitment, governance triggered only by regulator notice and one-time audits with no ongoing monitoring plan. Governance that stops at PowerPoint fails during the first real incident.
-
Do you handle EU AI Act compliance?
We implement controls that satisfy EU AI Act technical requirements (Articles 9-15 for high-risk systems). Legal classification of whether a system is high-risk, prohibited or limited-risk is a legal question for qualified counsel - we do not provide that opinion. Once classification is known, we implement the required technical controls.
The Pharos takeaway on AI governance consulting
Governance rewards teams that treat AI risk as architecture, not paperwork. Pharos leads with NIST AI RMF classification, structured model cards and documented incident response, and declines engagements where the goal is theatre rather than measurable risk reduction[8].
Book a 30-minute AI governance readiness call
Your business results matter
Achieve them with minimized risk through our bespoke innovation capabilities
What happens next?
-
Contact us
Contact us today to discuss your project. We're ready to review your request promptly and guide you on the best next steps for collaboration
Same day -
NDA
We're committed to keeping your information confidential, so we'll sign a Non-Disclosure Agreement
1 day -
Plan the Goals
After we chat about your goals and needs, we'll craft a comprehensive proposal detailing the project scope, team, timeline and budget
3-5 days -
Finalize the Details
Let's connect on Google Meet to go through the proposal and confirm all the details together!
1-2 days -
Sign the Contract
As soon as the contract is signed, our dedicated team will jump into action on your project!
Same day